
Provider Keys is not yet available on every account. If Provider Keys
does not appear in Settings,
contact the Fireworks team to enable it.
Self-serve setup is coming soon. Until then, send a per-request Anthropic or
OpenAI header from APIs and SDKs or
LLM Gateways. For
coding harnesses, review local support in
Harness Compatibility.
fireconnect login. The provider key stays with the account, so it is never distributed to developers or pasted into a chat. Fireworks encrypts API keys at rest and never shows them in full again. IAM role ARNs are non-secret identifiers.
Router availability in FireConnect varies by harness. See
Harness Compatibility for current support.
Provider Keys is an account-admin-only feature. You must be an account admin
to connect, replace, or remove a key, whether from the dashboard or through
firectl.Check provider support and connection states
Provider Keys supports these providers:- One active key per provider: You can upload several keys for one provider, but only one can be active for routing at a time.
- Bedrock also needs routes: a Bedrock key is not enough. Each model you want to send through your AWS account needs a Bedrock model ID and region. See Amazon Bedrock Setup.
Connect a key in the dashboard
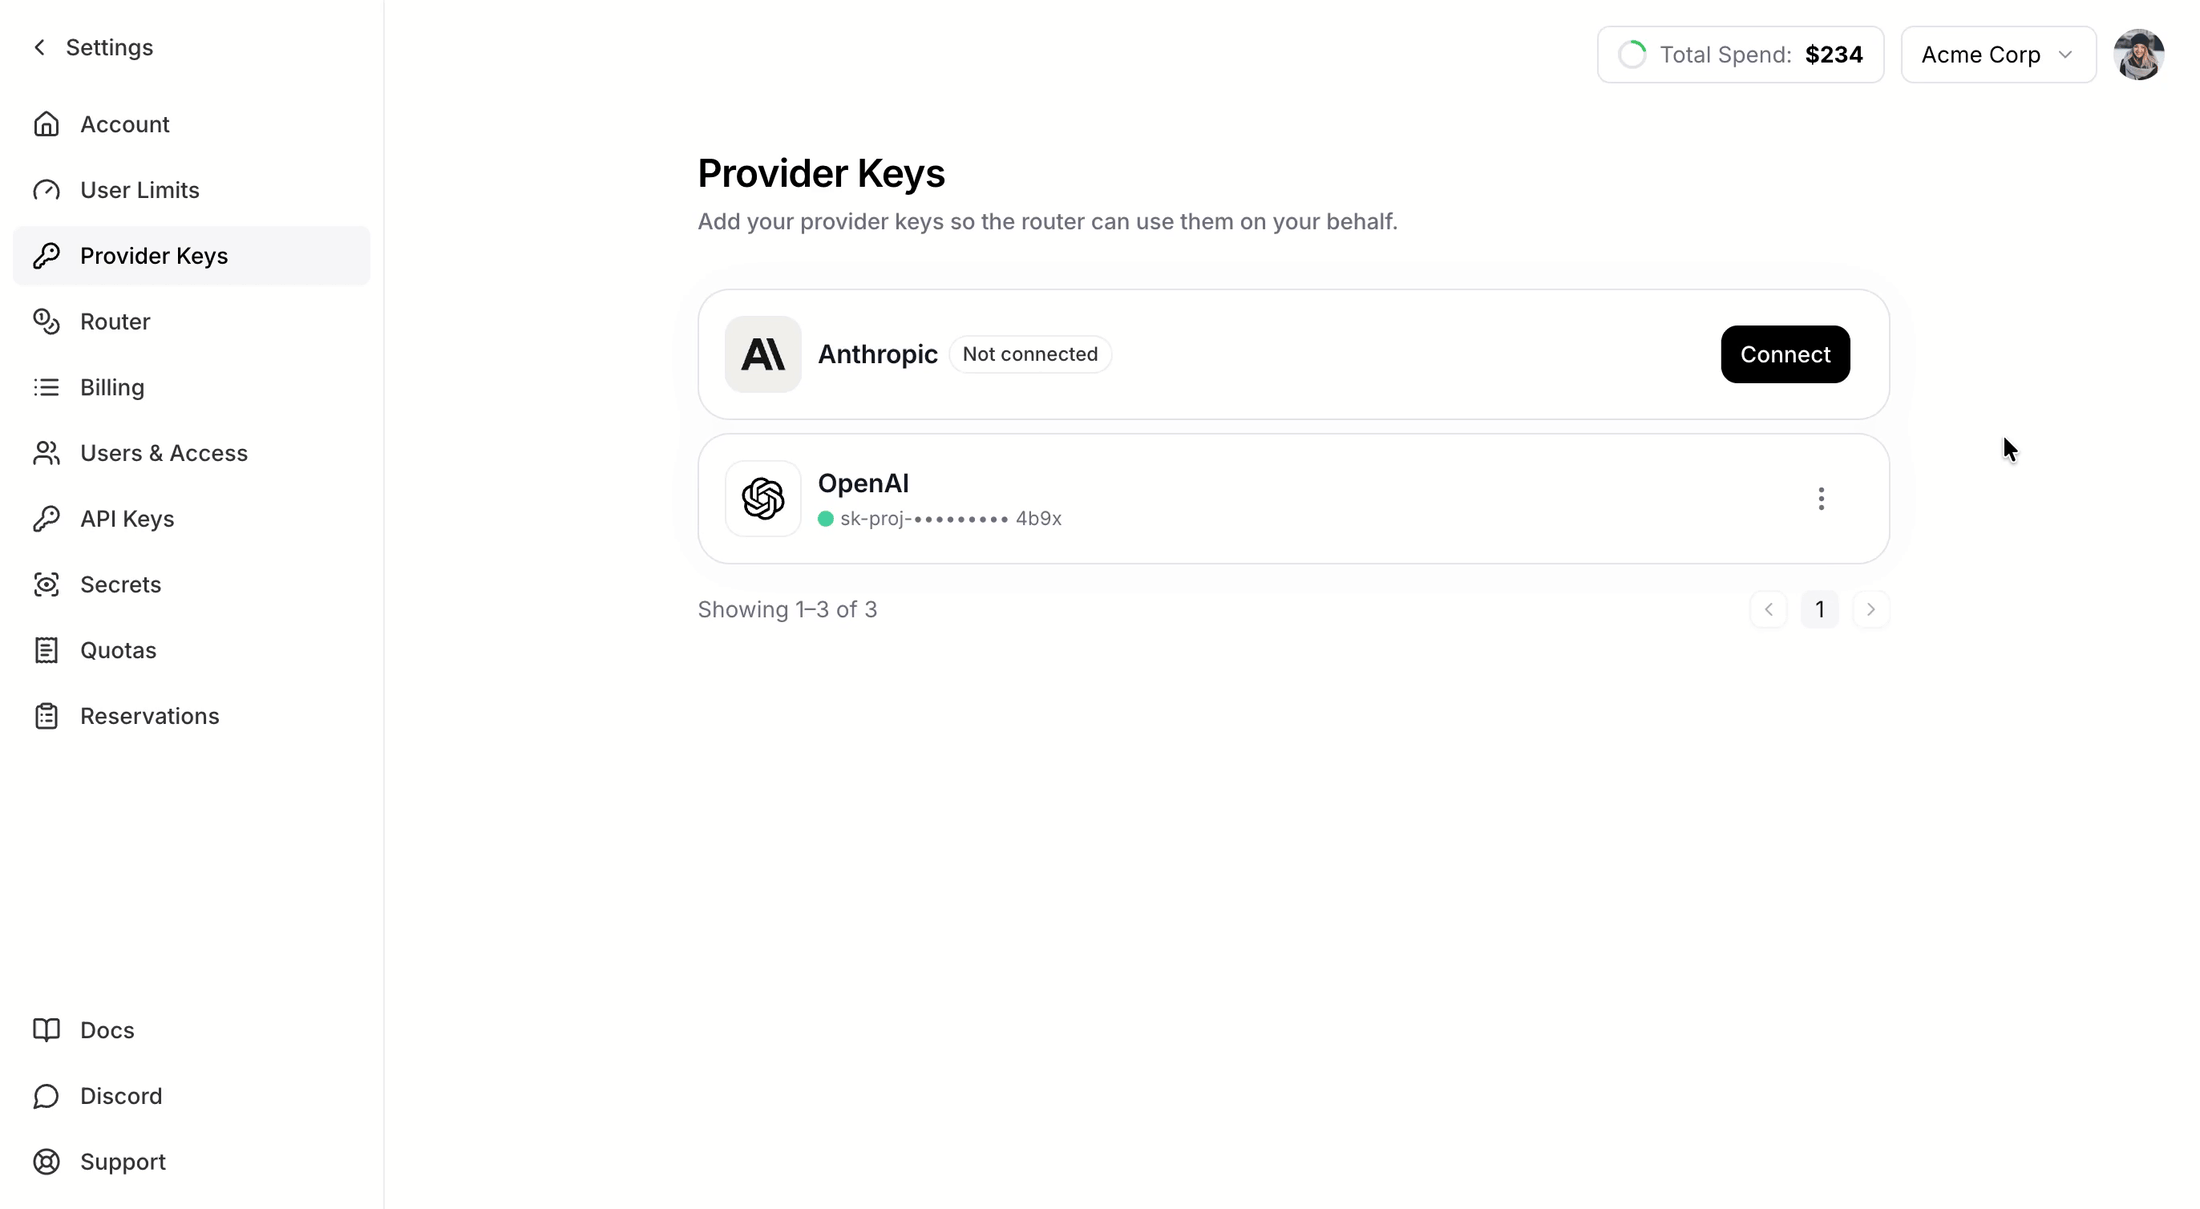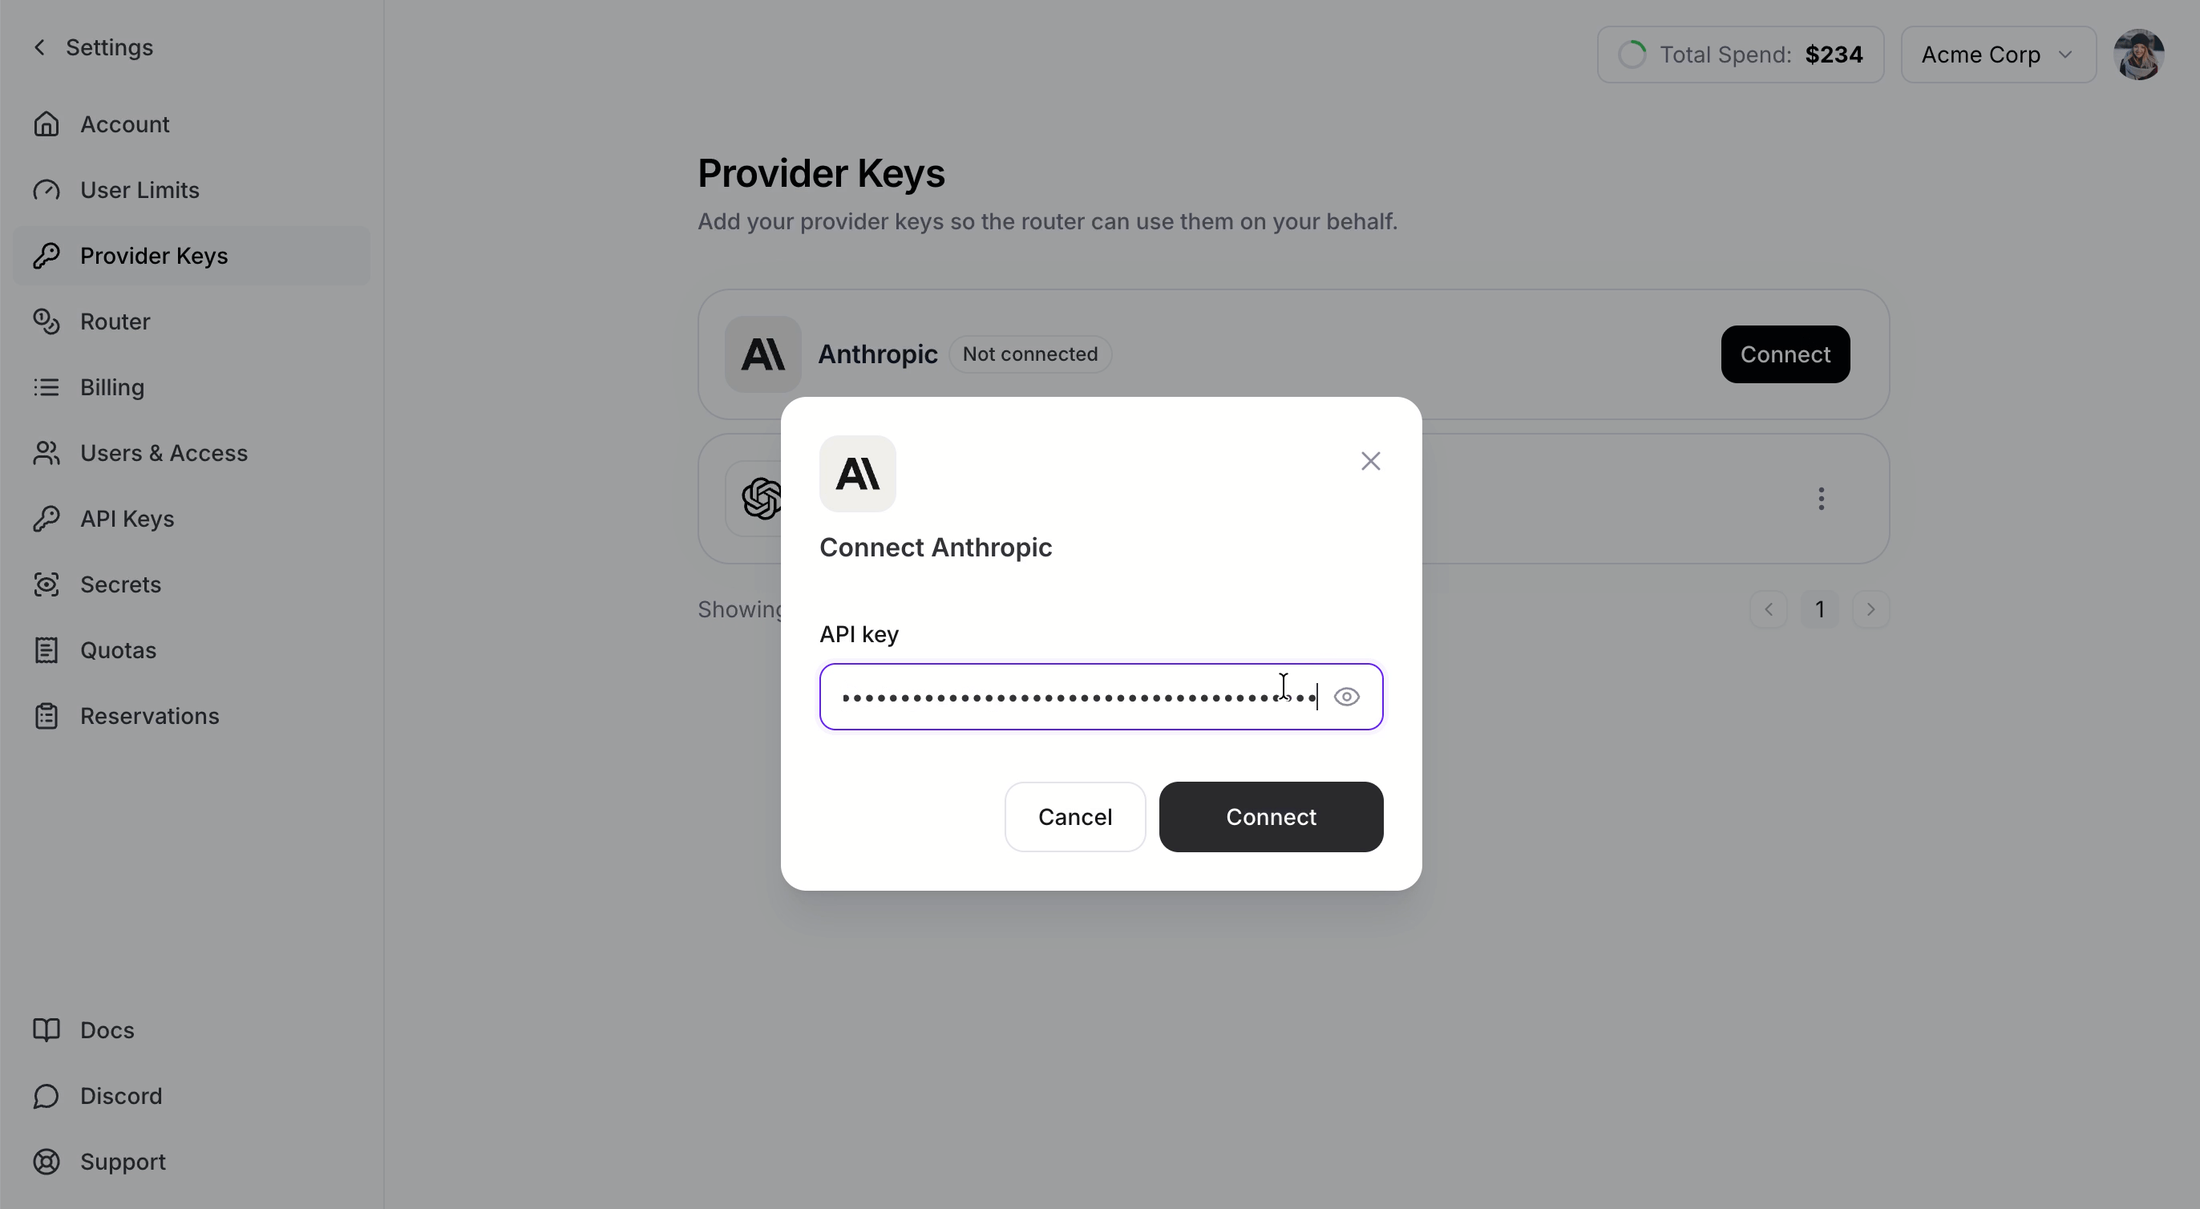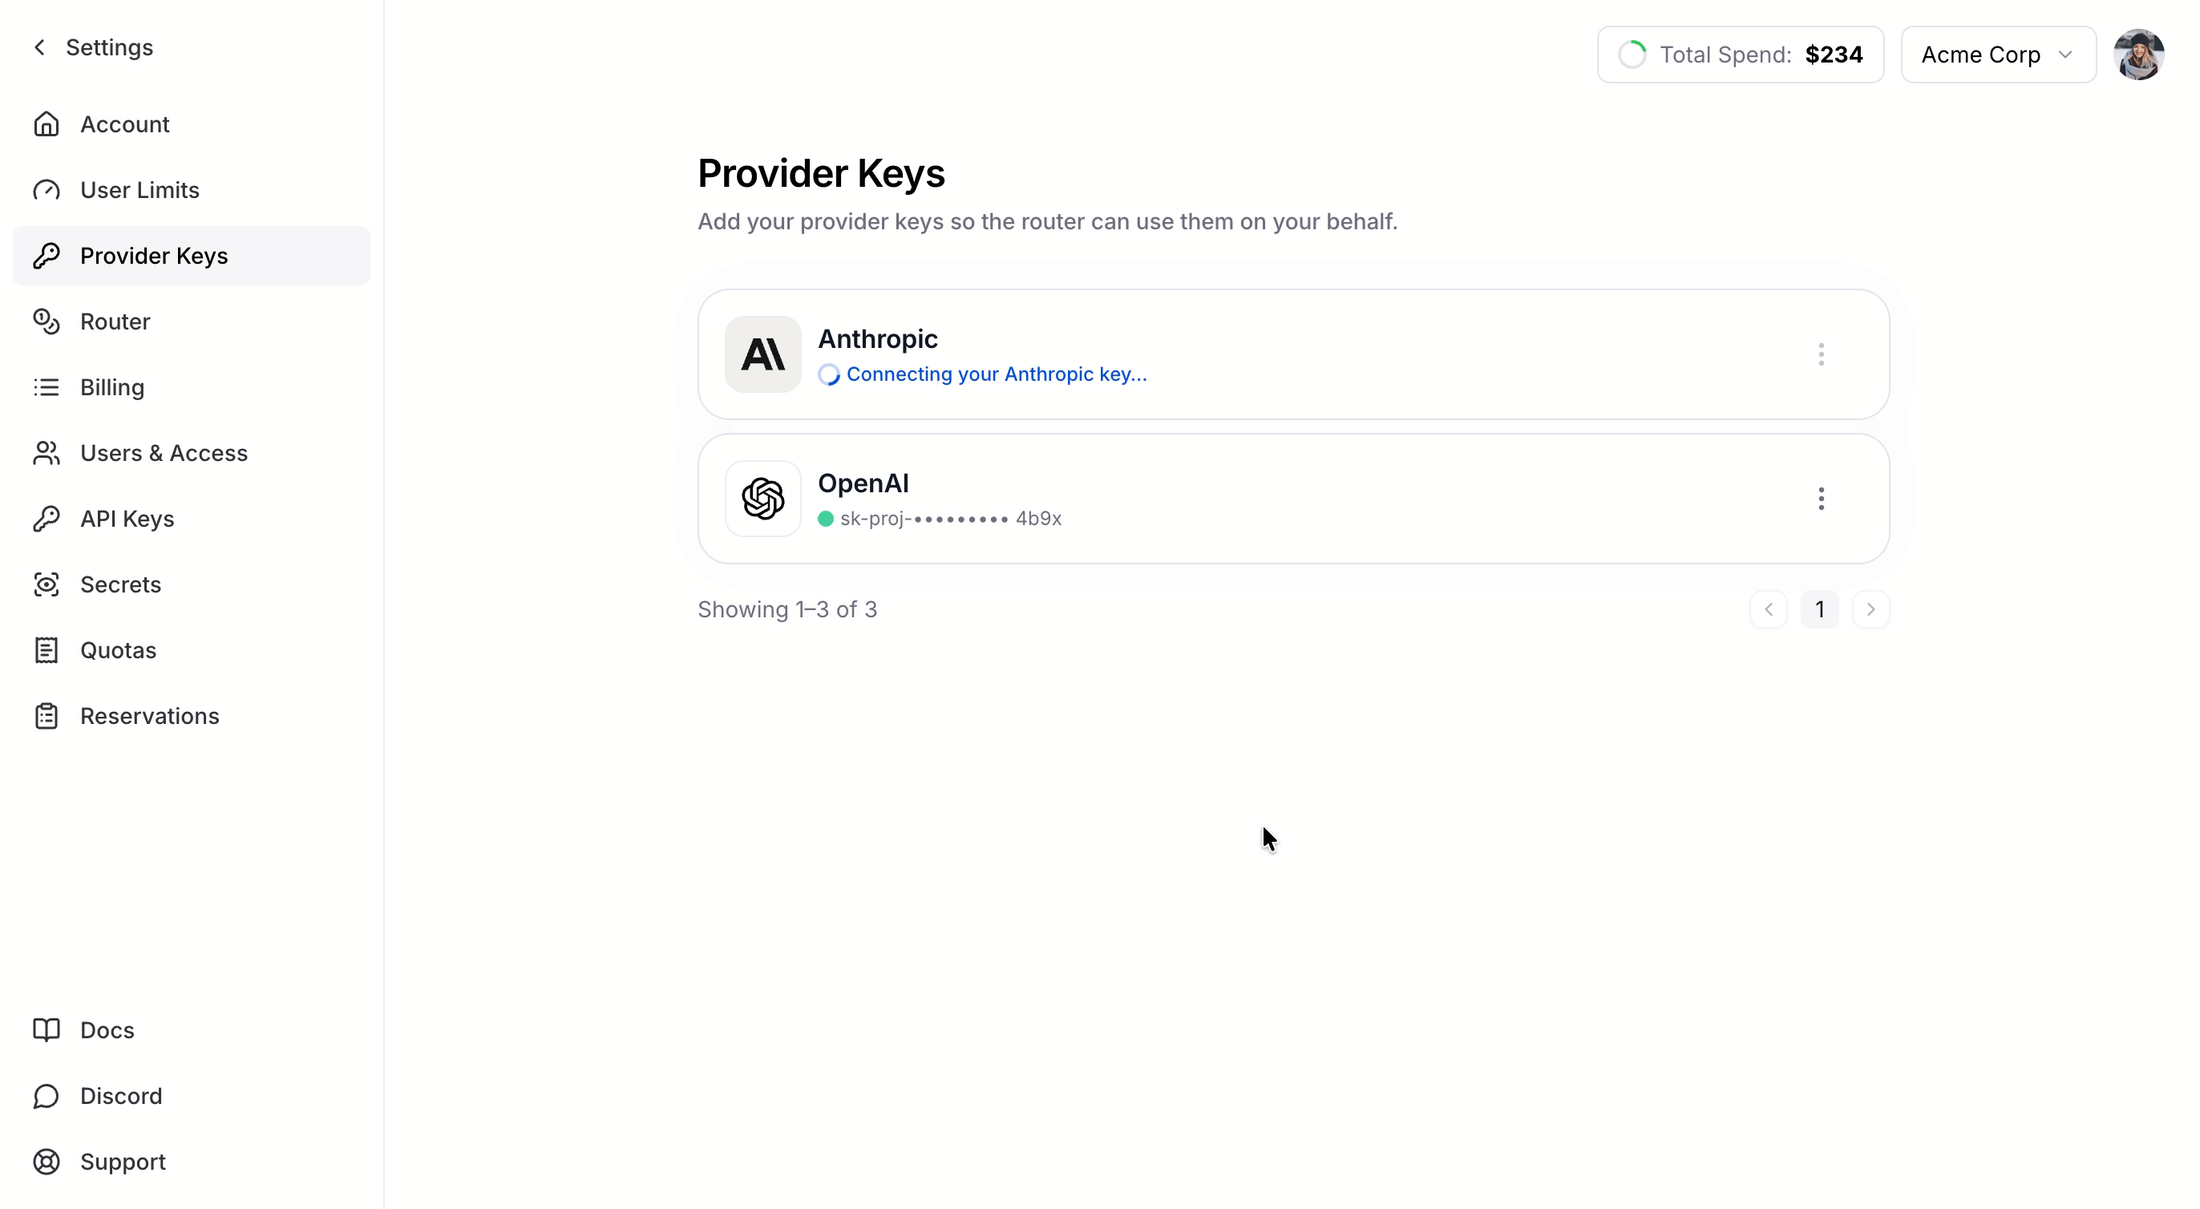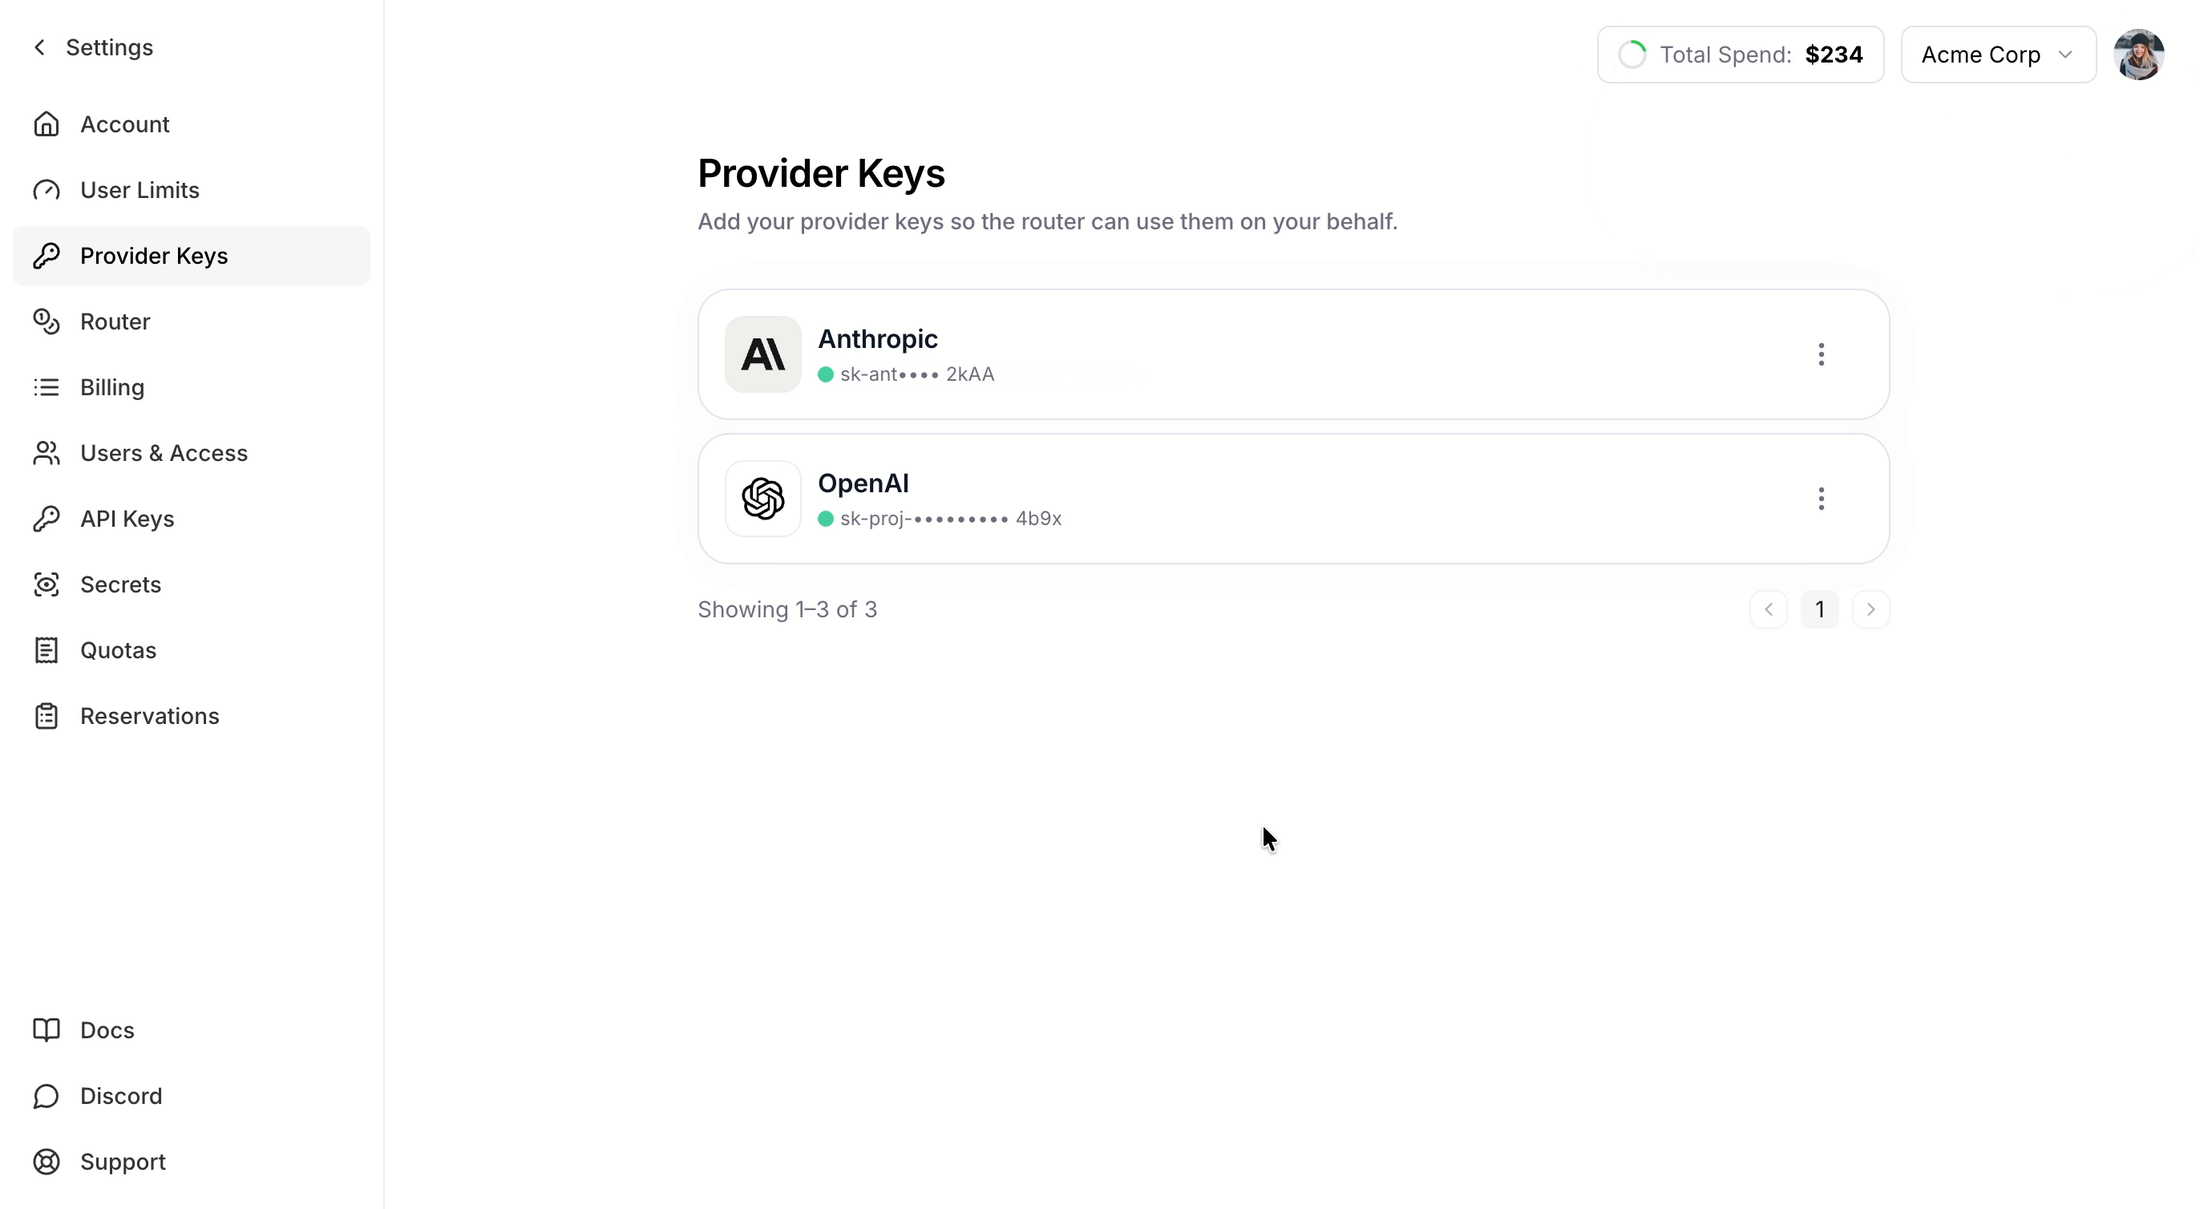
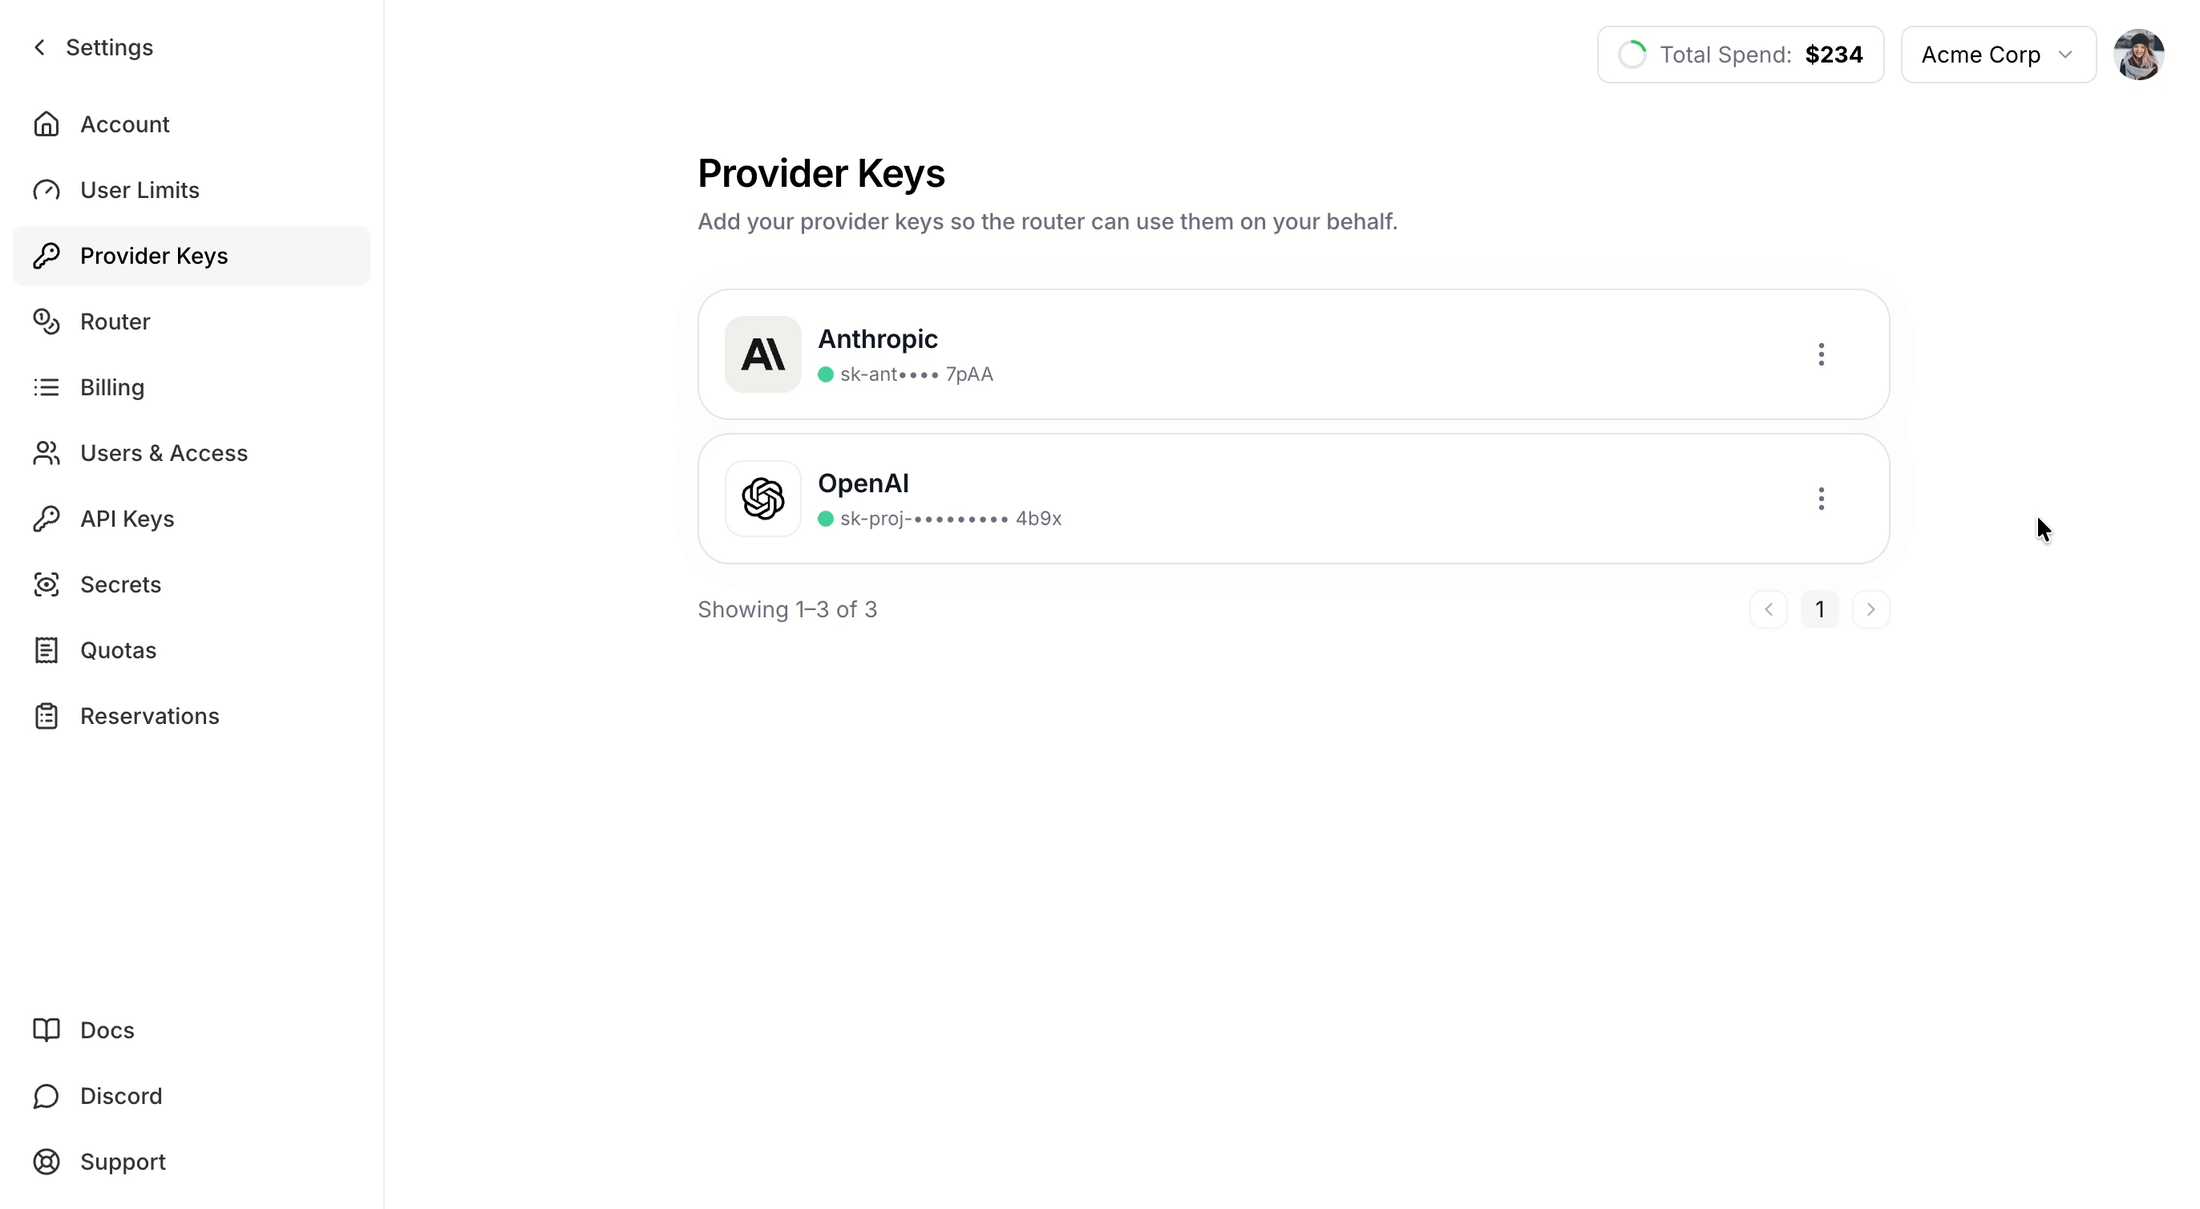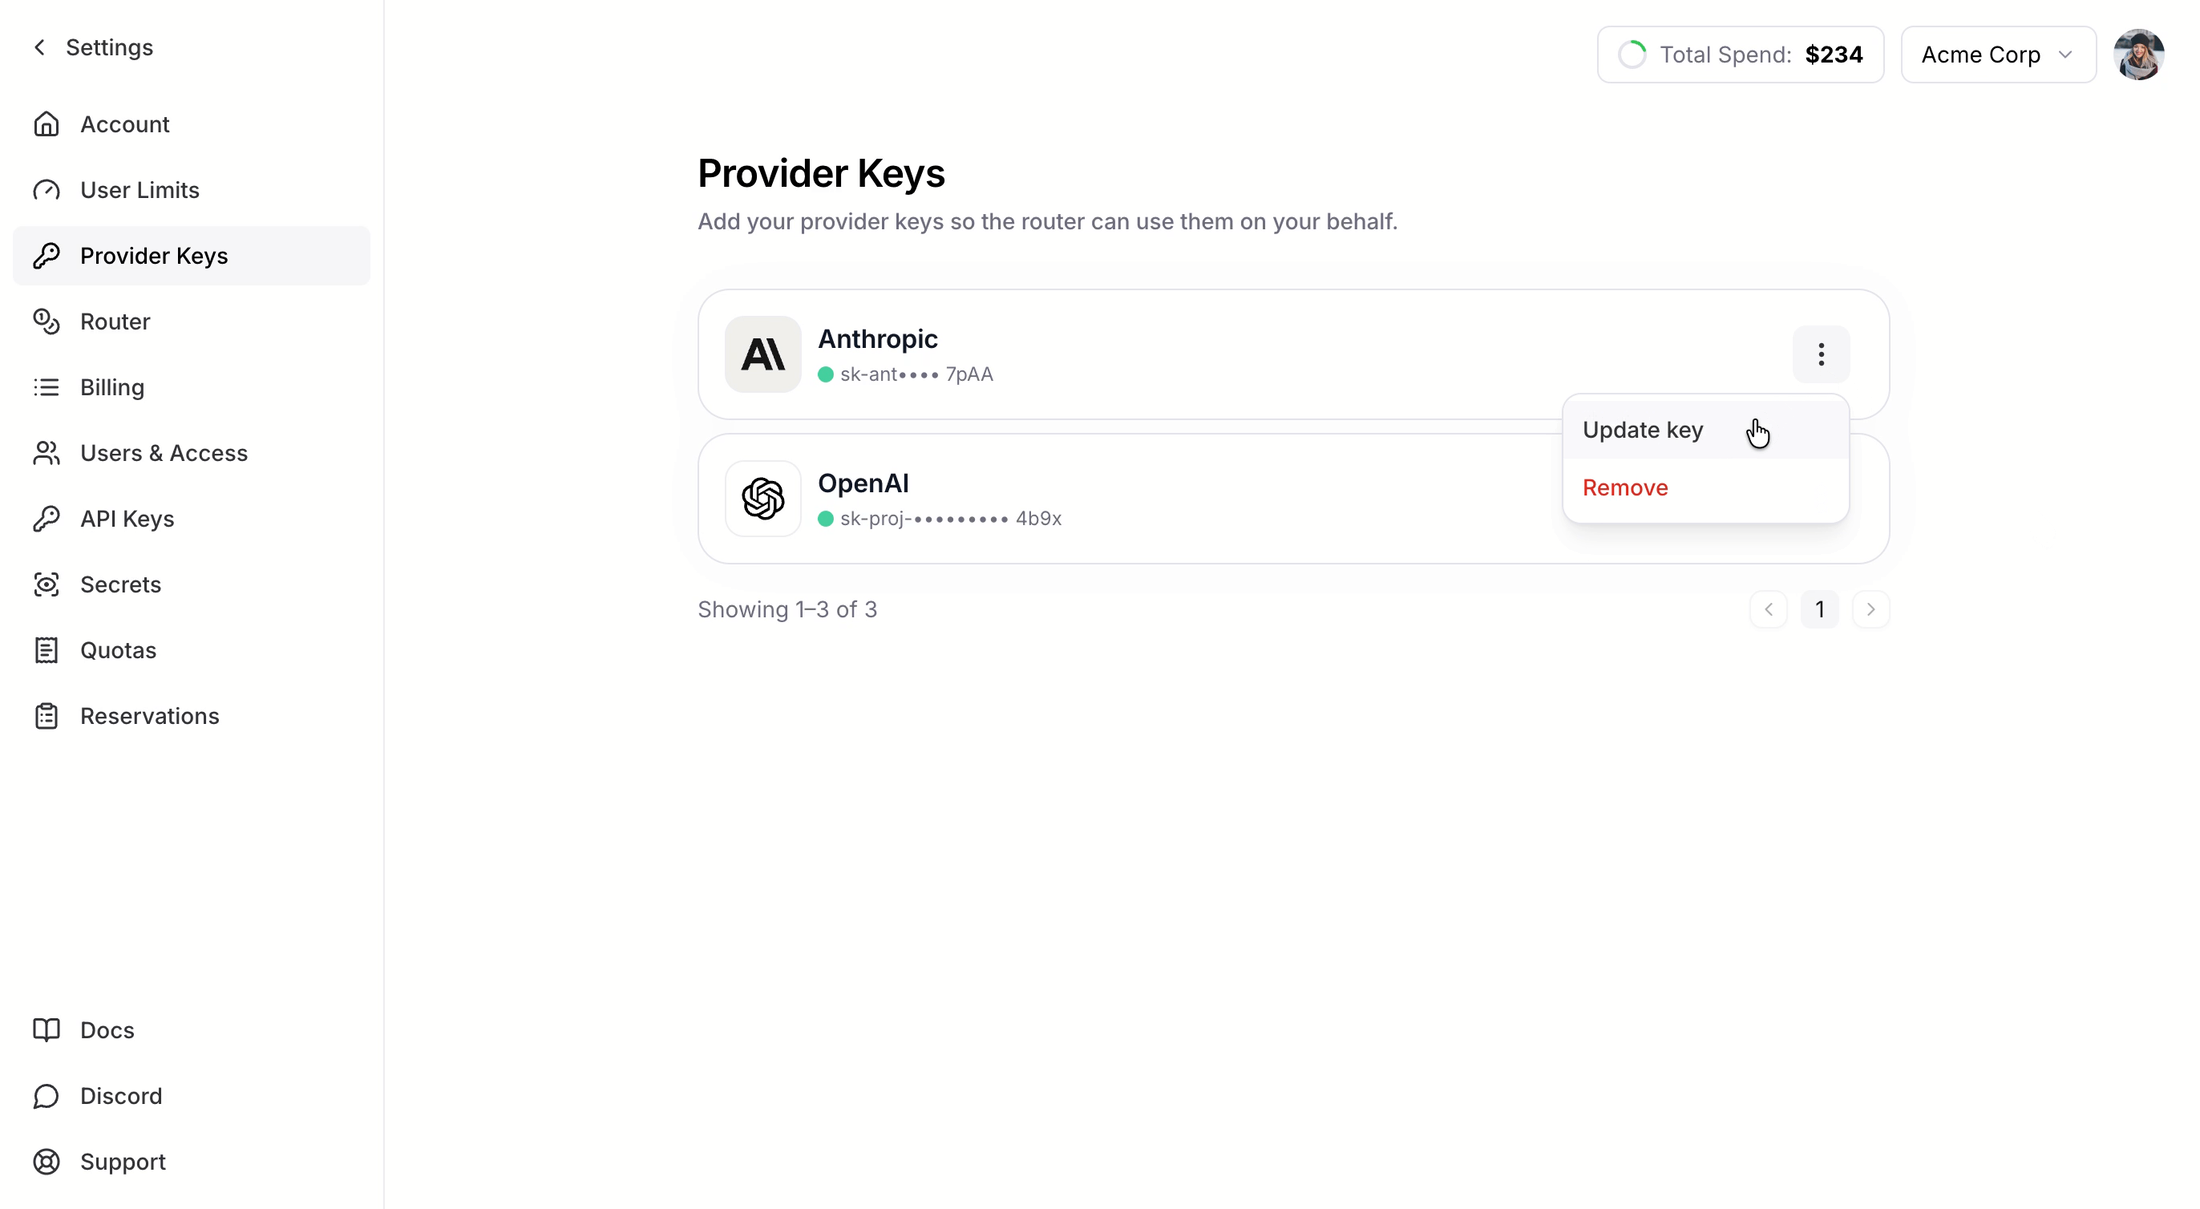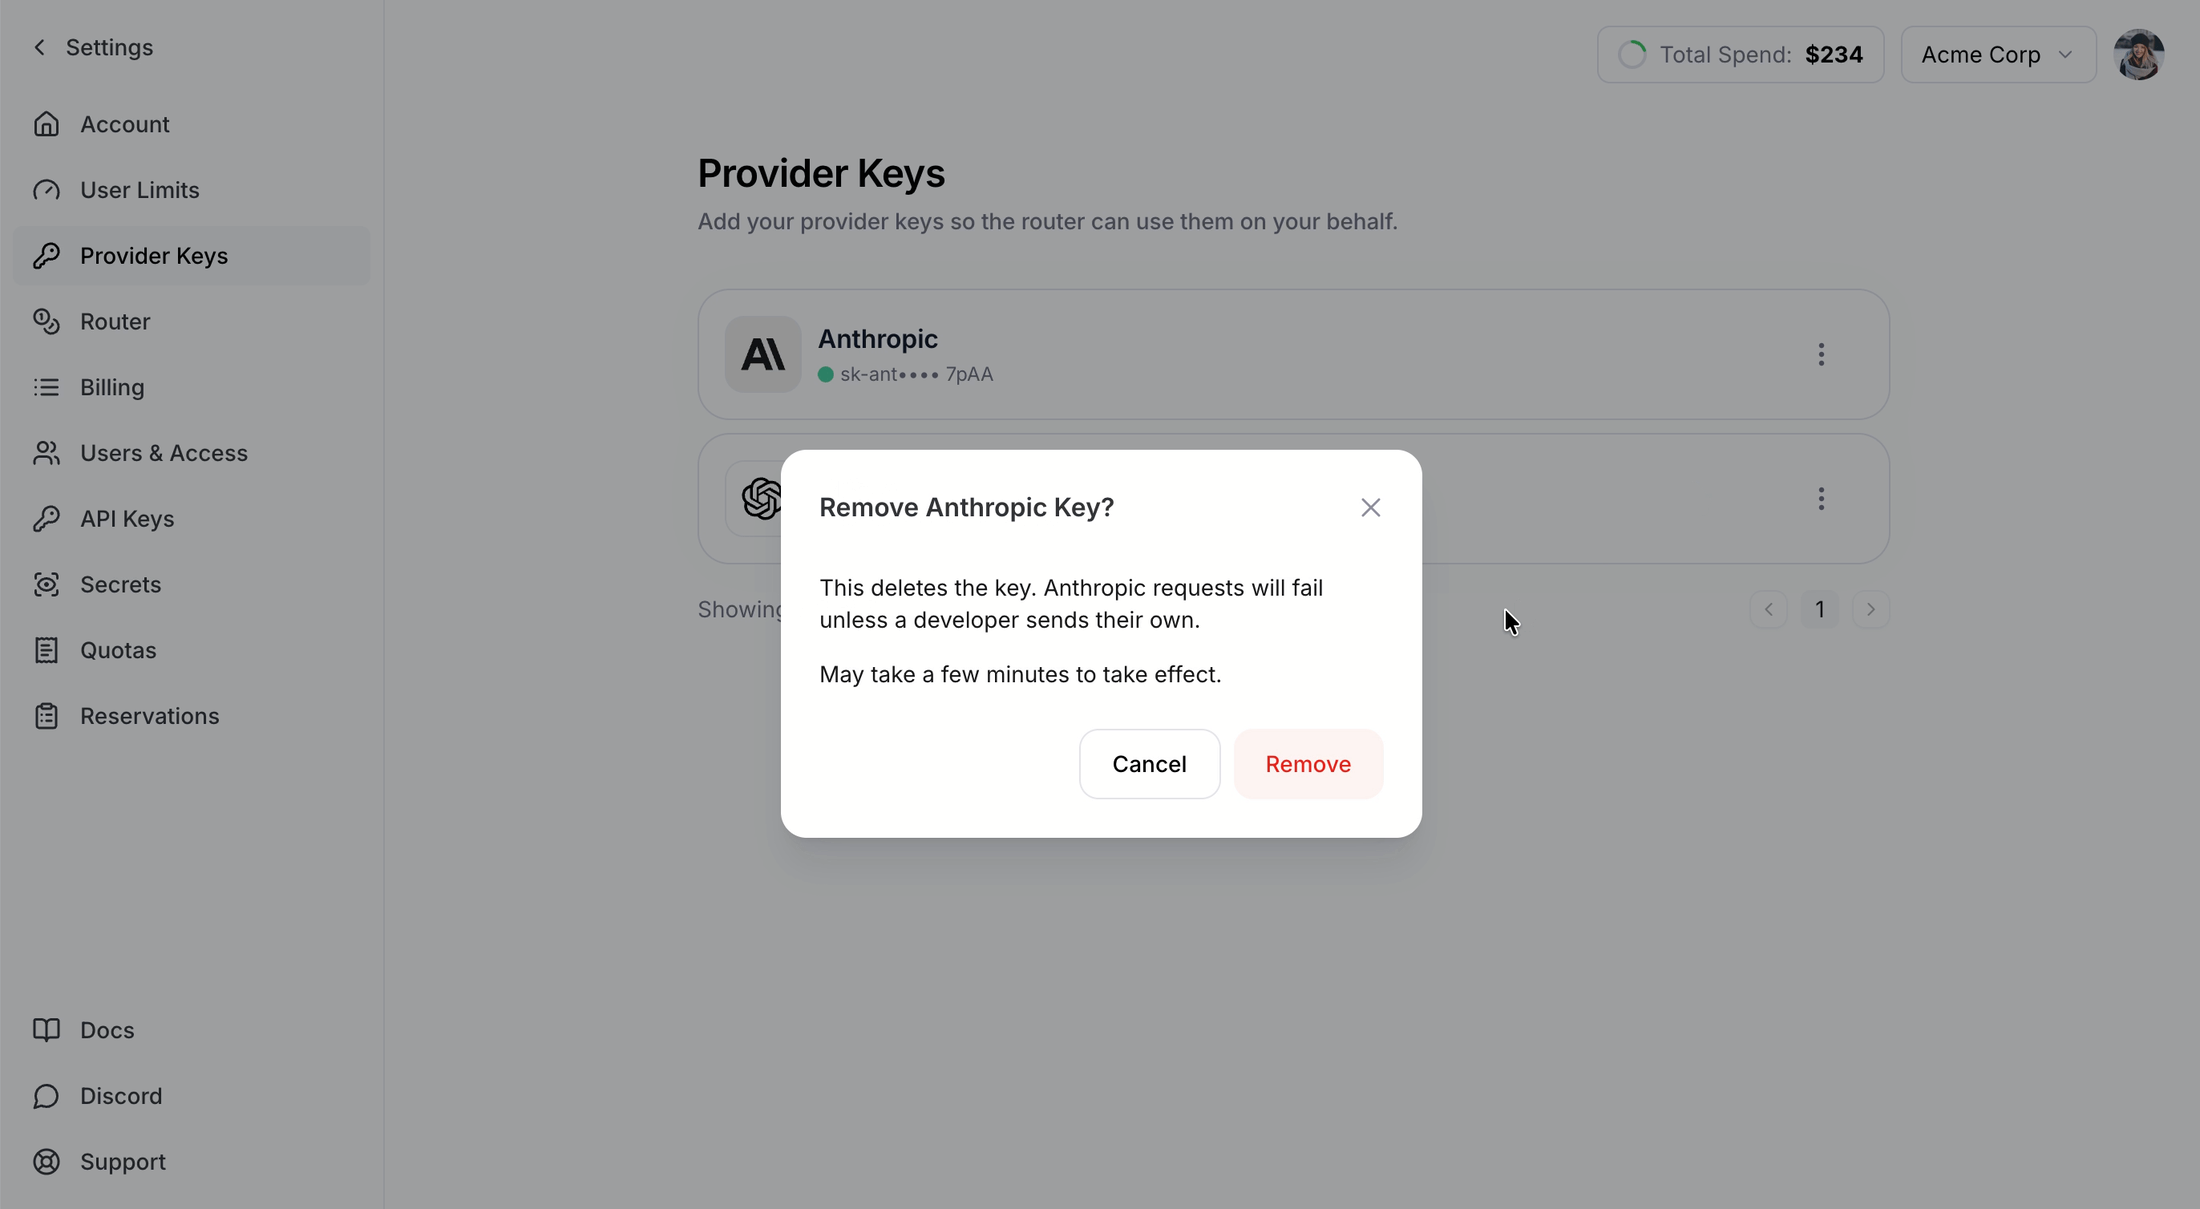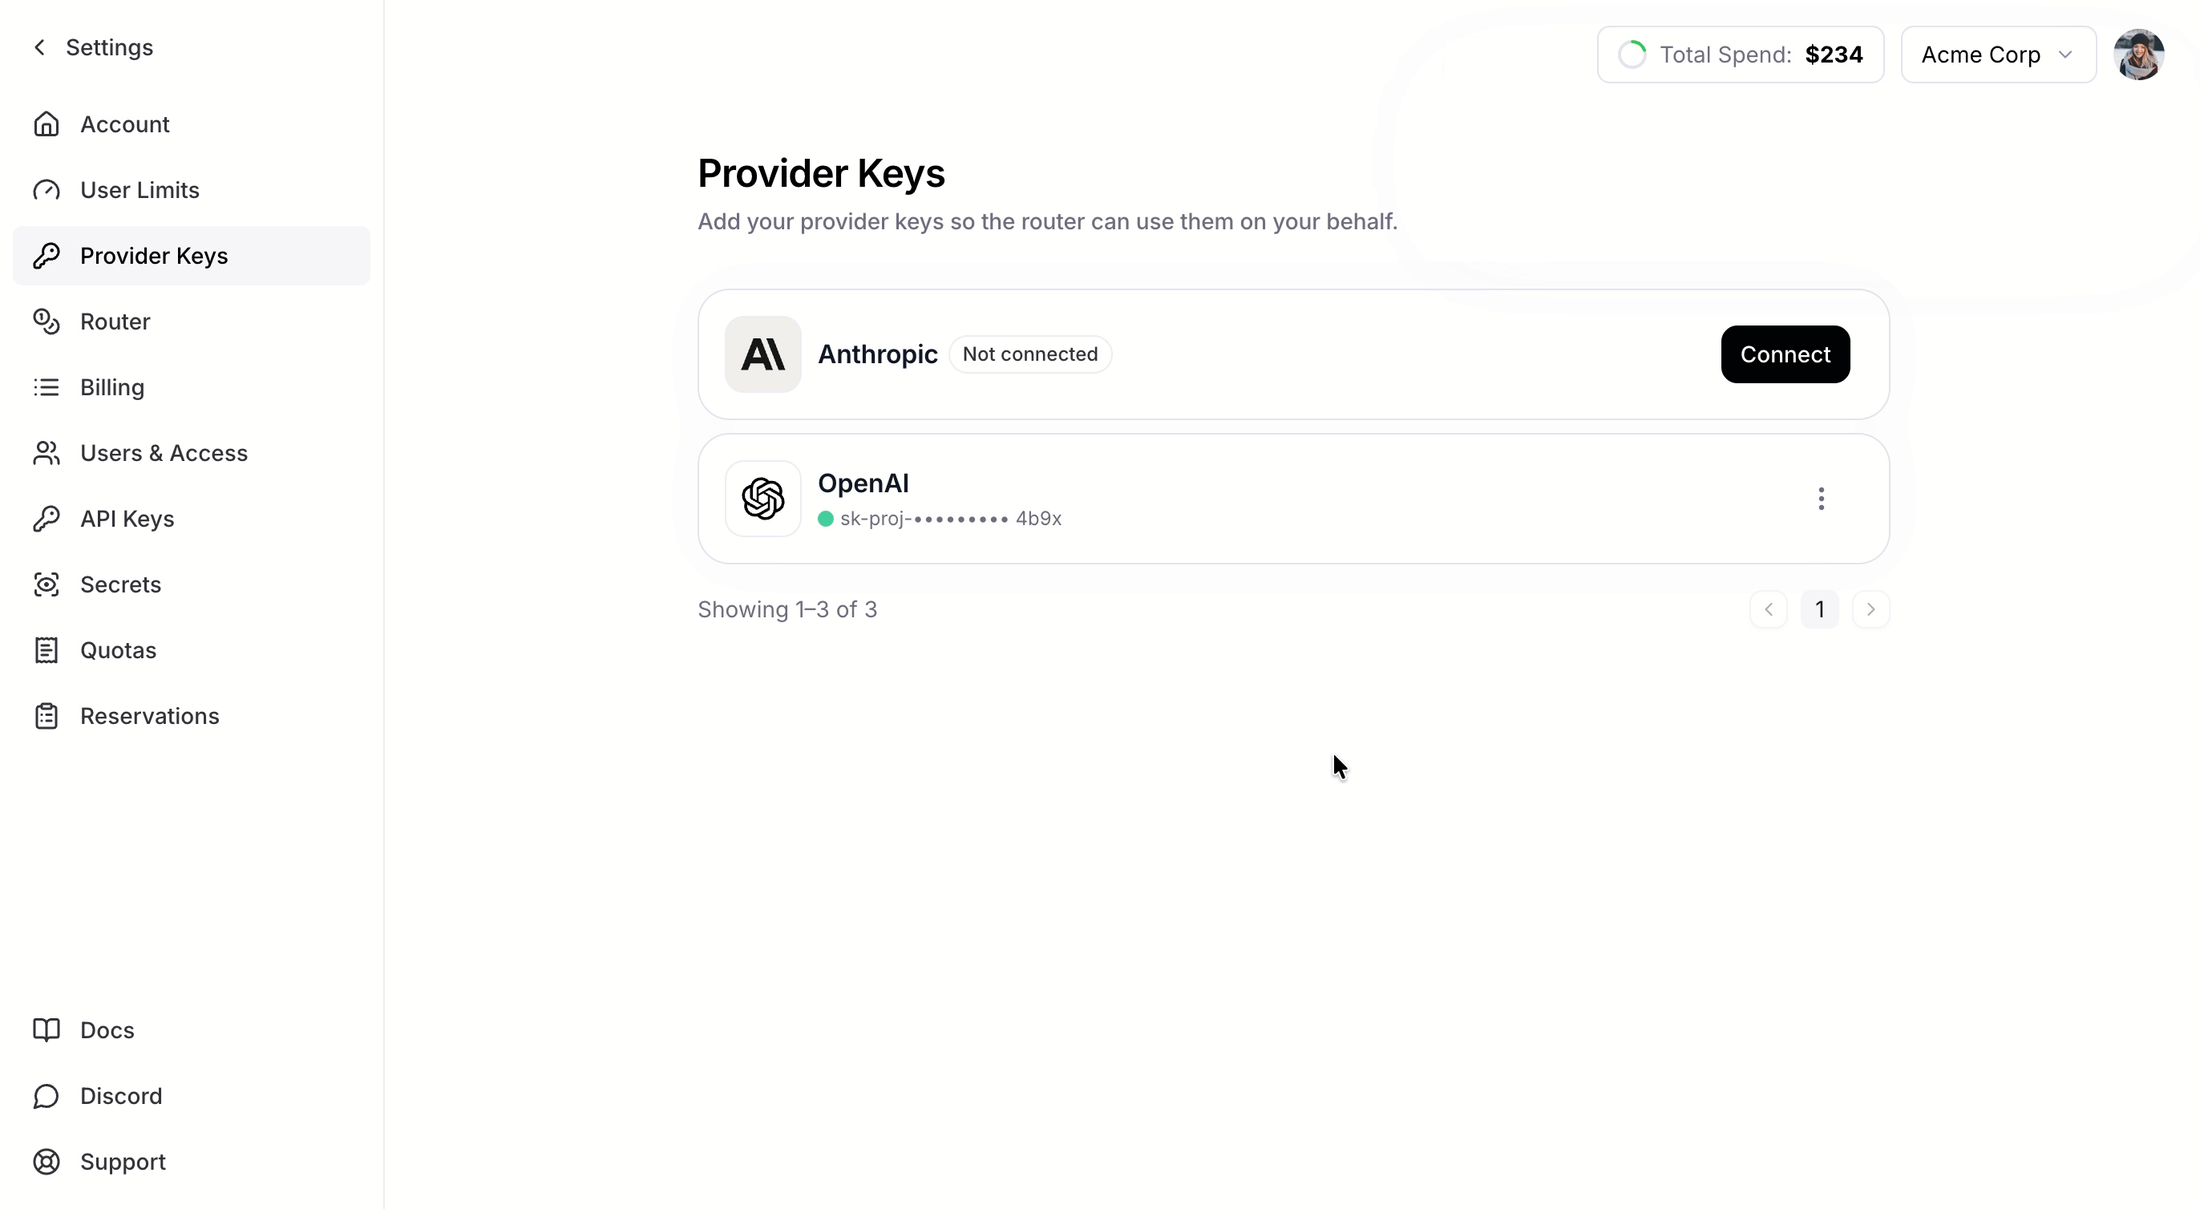
Connect a Provider Key from Settings without using a terminal. You can open Provider Keys directly.1
Open Provider Keys
Open Settings and go to Provider Keys, or open the Provider Keys page directly.
2
Connect a provider
Find the provider you want (Anthropic, OpenAI, or Amazon Bedrock) and click Connect.
3
Paste your key
For Anthropic or OpenAI, paste your key and click Connect. You will see a confirmation once it is saved.For Amazon Bedrock, choose an IAM role or API key, then select models. After the card connects, fill in each model’s Bedrock model ID and region, then click Save. Full steps are in Amazon Bedrock Setup.
Replace or remove a key
Open the menu on any connected provider to:- Replace: swap in a new API key or IAM role ARN for that provider. Bedrock routes stay in place when you update only that value.
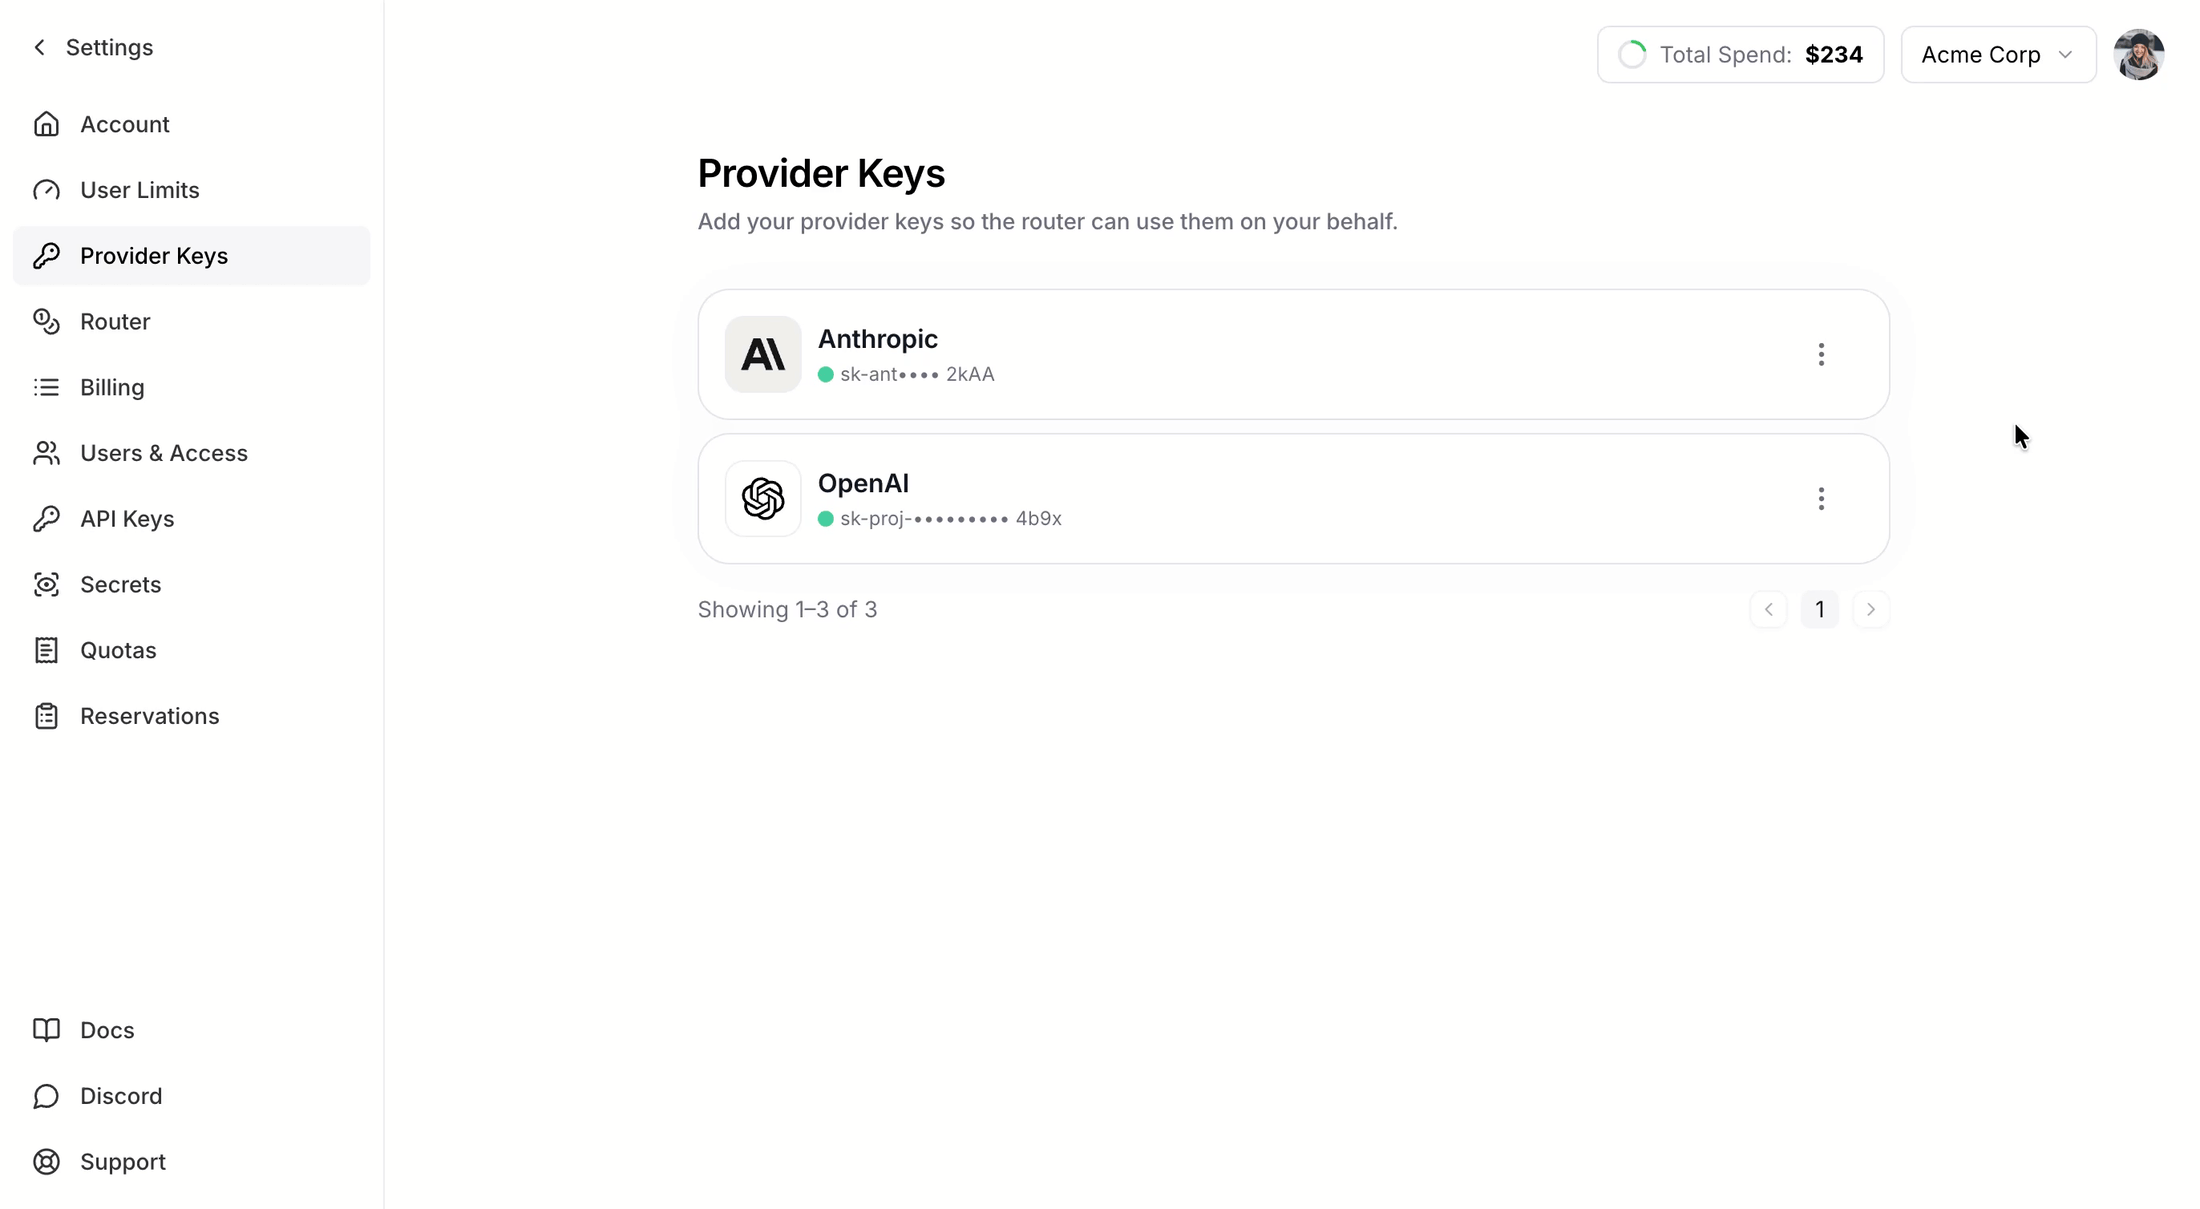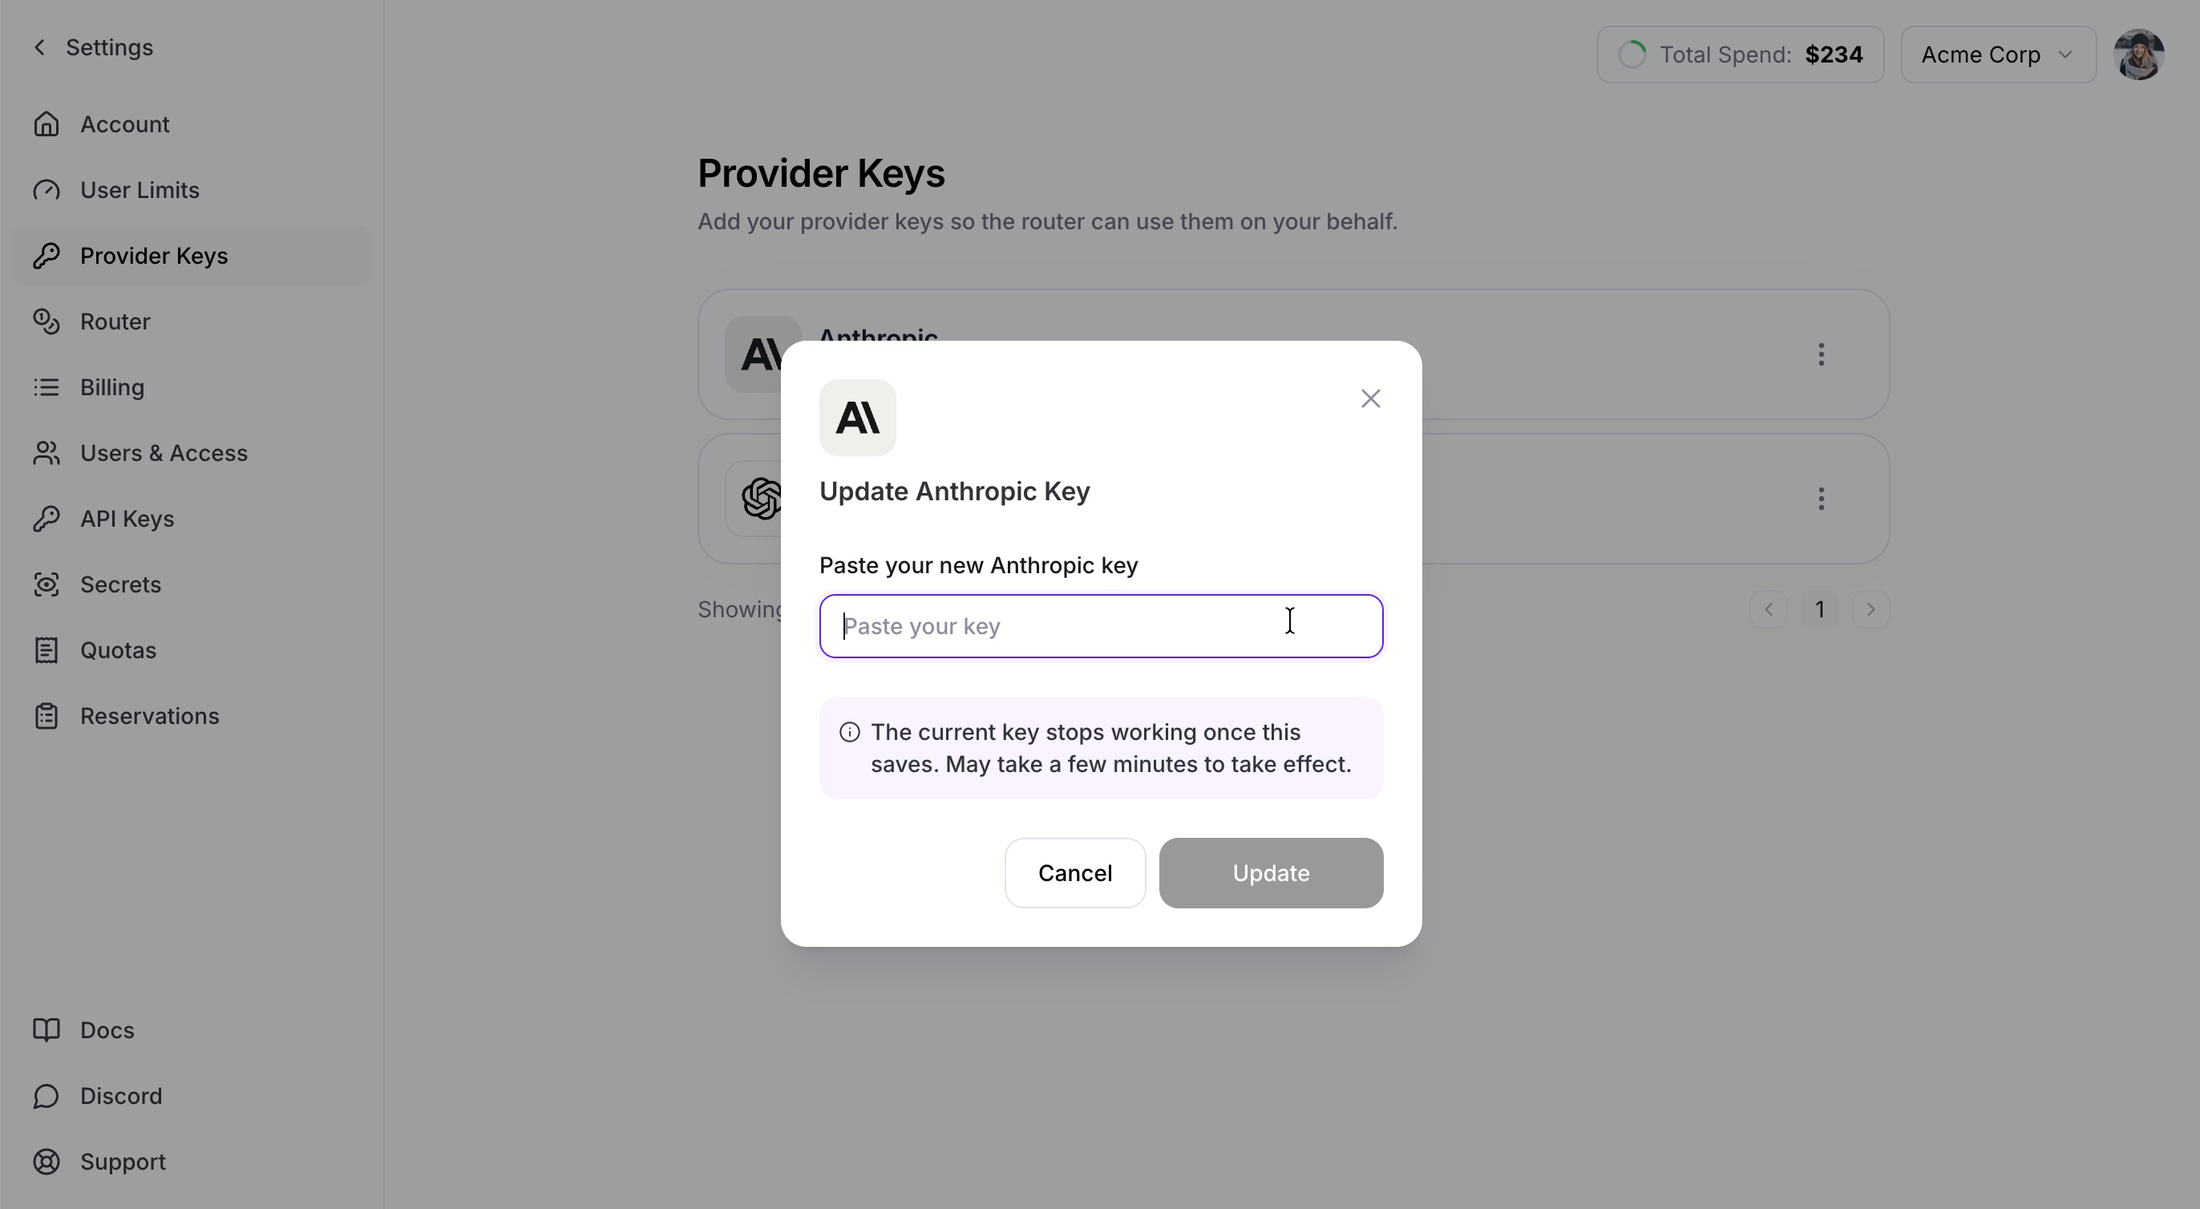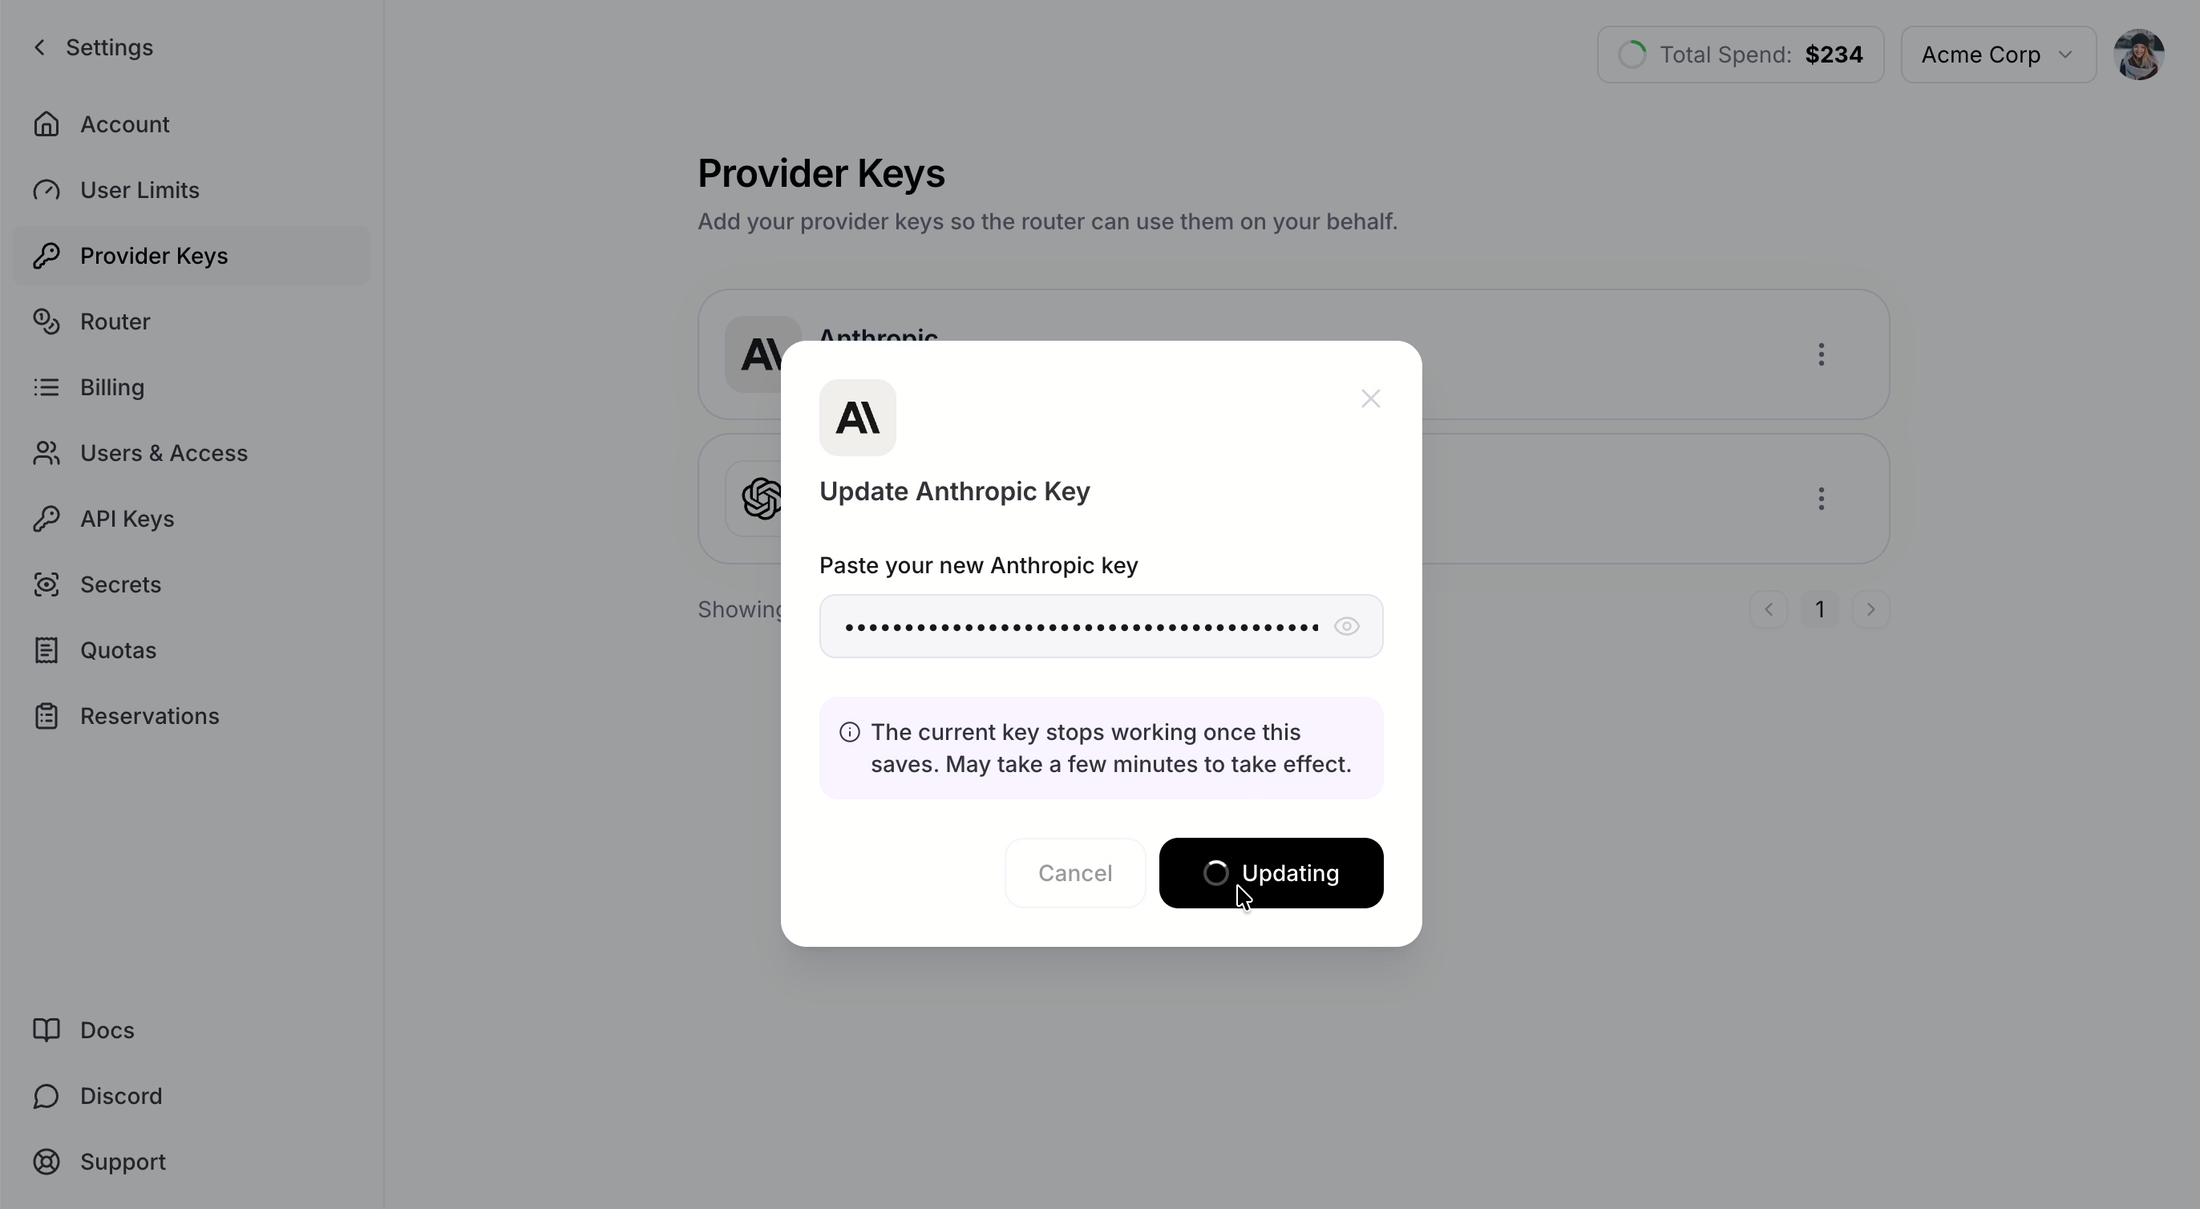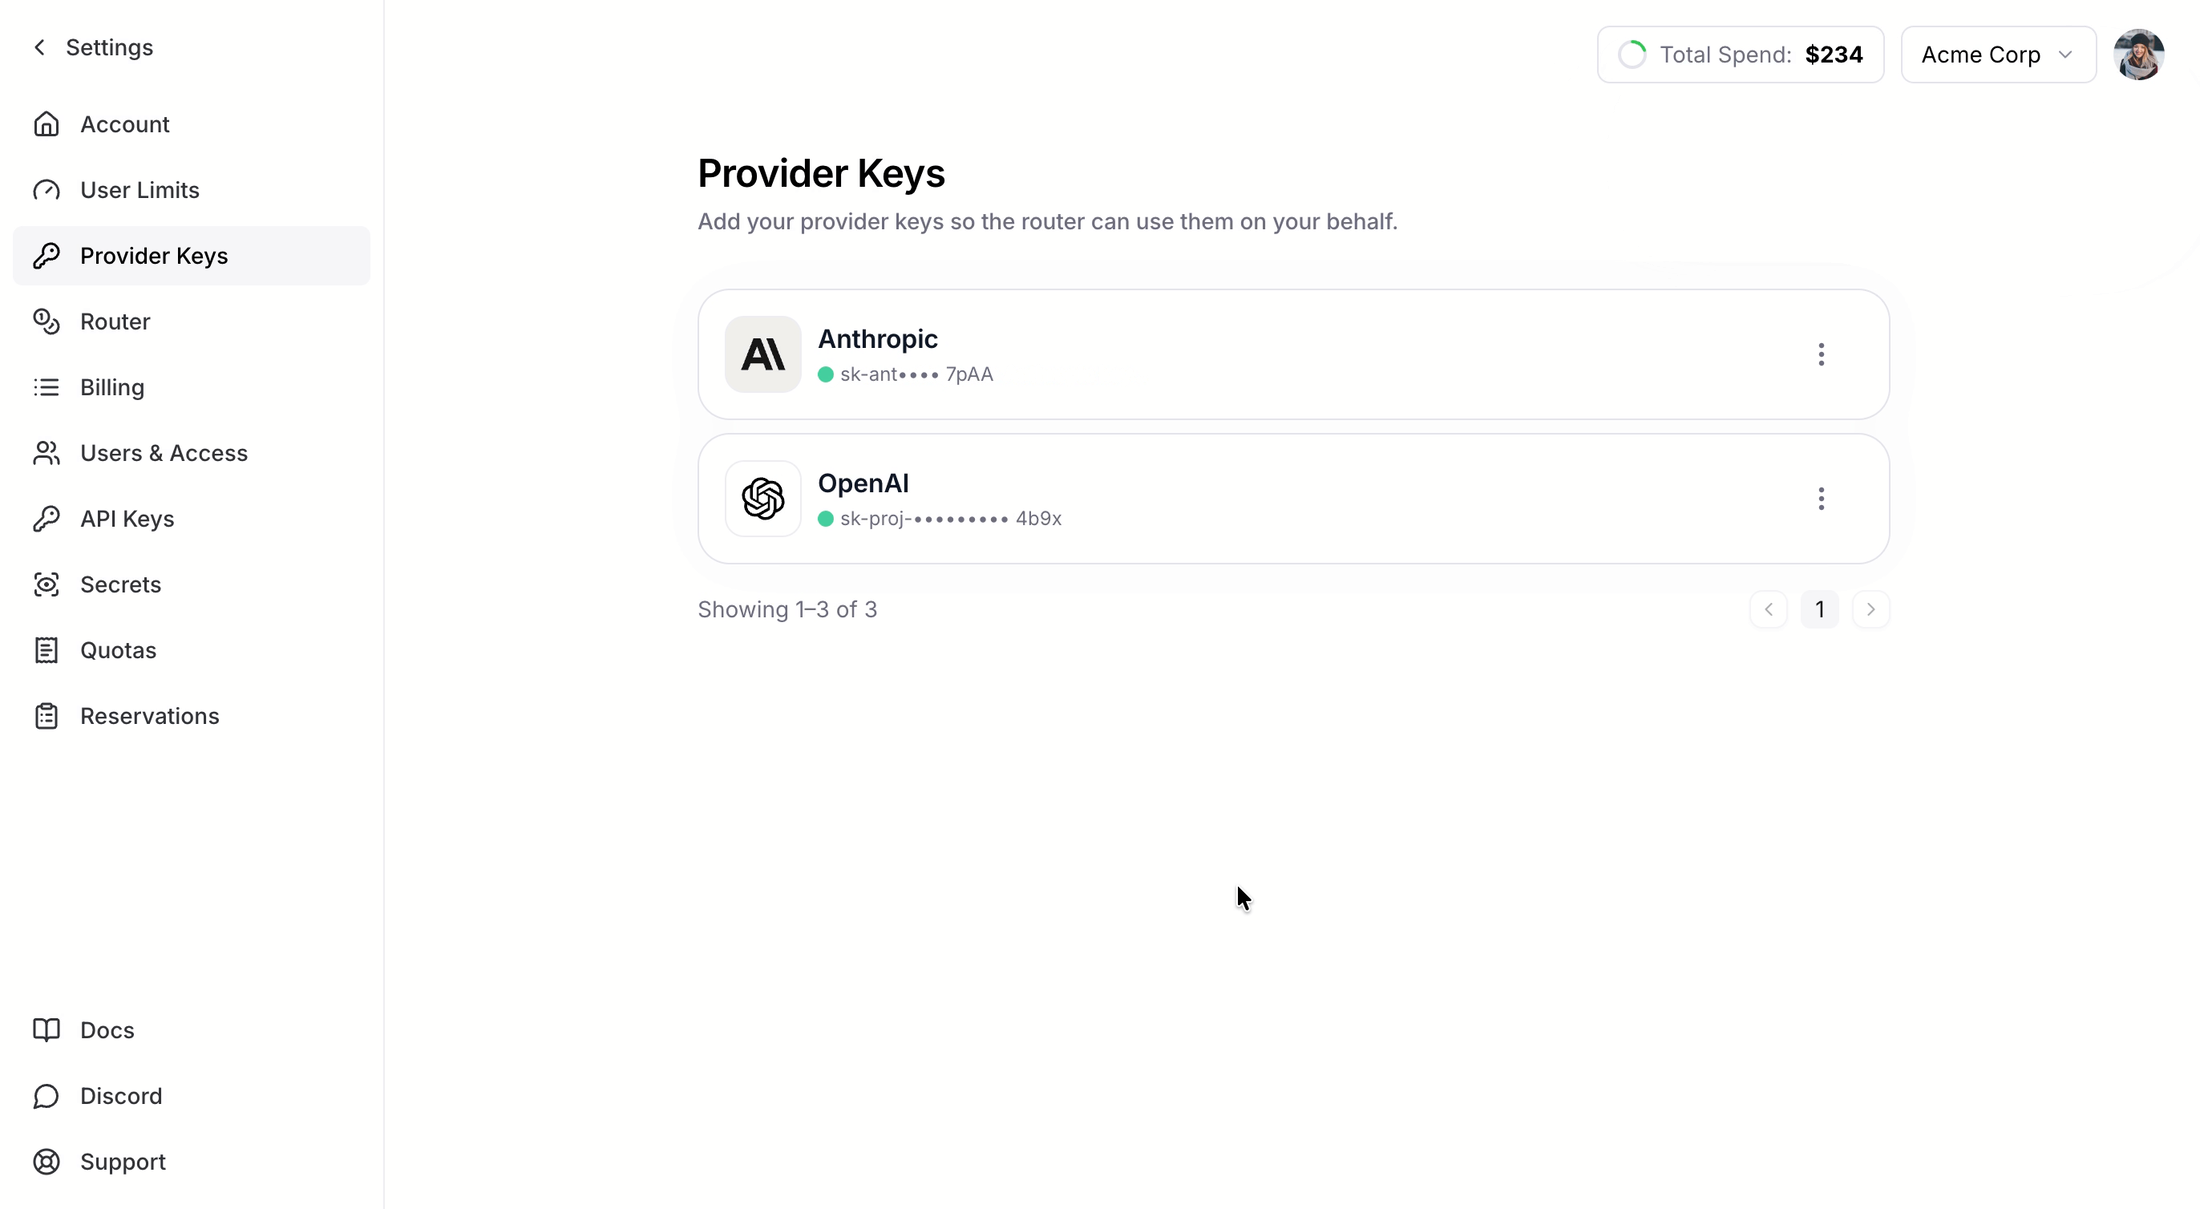
- Remove: remove the key. For Bedrock, this also deletes every Bedrock route.
Manage keys with firectl
You can also connect, replace, remove, and inspect Provider Keys with firectl. Use firectl provider-key to manage stored keys and firectl provider-key-binding to choose which key is active for routing. firectl firerouter-provider-key is an alias.
The CLI can also stop using a key for routing without deleting it (provider-key-binding unbind). The key remains stored, so you can bind it again without re-uploading it.
Add or replace a key
upload stores a key but does not make it active for routing. Use bind to make it active. --provider-type is required and accepts anthropic, openai, grok, or bedrock.
For the quickest Anthropic or OpenAI setup, pass an environment variable to --api-key. This keeps the value out of your shell history:
--from-file. The file should hold only the raw key, with no JSON or quotes. firectl trims surrounding whitespace:
On a shared or multi-user machine, prefer
--from-file. The shell expands
$ANTHROPIC_KEY before firectl starts, so --api-key keeps the key out of
your shell history but still exposes it in the process list (ps) while the
command runs. --from-file passes only the path.--from-file or an IAM role with --aws-iam-role-arn, then bind with --routes-file. Omitting --routes-file binds an empty route set, which serves no Bedrock traffic and replaces any existing routes. See Amazon Bedrock Setup.
Check status
provider-key list shows each stored key’s ID, provider, credential type, preview, and display name. API key previews are masked; IAM role previews show the full non-secret role ARN. provider-key-binding list and get show each provider’s connection state, credential type, and active PROVIDER_KEY resource name. For Bedrock, also confirm that routes lists every model you intend to send through AWS.
Delete a key
Use the key ID or full resource name fromupload or provider-key list. If that key is live for the provider, unbind it first. Unbind stops routing from using it; the key stays stored until you delete it.
Key behavior and security
- Request-level credentials take precedence when supported. If a request includes a provider key, that key is used and the stored one is skipped.
- Changes are not instant. After you connect, replace, or remove a key, allow 30–60 seconds for the change to reach requests.
- Your API key stays private. The full API key is stored securely and never returned. For API keys, the dashboard and API only show the provider, state, masked preview, and dates. An IAM role ARN is a non-secret identifier and is returned as the credential preview.